

Zone-Based Firewall
Clear security zones for clients, servers, IoT, guests, cameras and management - with understandable rules instead of established exceptions.
Ubiquiti Partner · Certified employees · Switzerland-wide
Ubiquiti Cloud Gateway, UniFi Firewall, VPN and SD-WAN in a secure architecture - from Swiss SMEs to highly available enterprise networks.
 Ubiquiti Enterprise PartnerCertified advice from novoSYS

From the compact 2.5G console to the highly available enterprise firewall: novoSYS dimensions throughput, number of clients, storage, WAN redundancy and security services together.

 Compact2.5G
For smaller sites with a multi-gigabit network and a need for a compact UniFi console, optionally with camera recording..
 Performance10G
For compact sites with fast internet or a 10G connection to the internal network, without a large rack gateway..
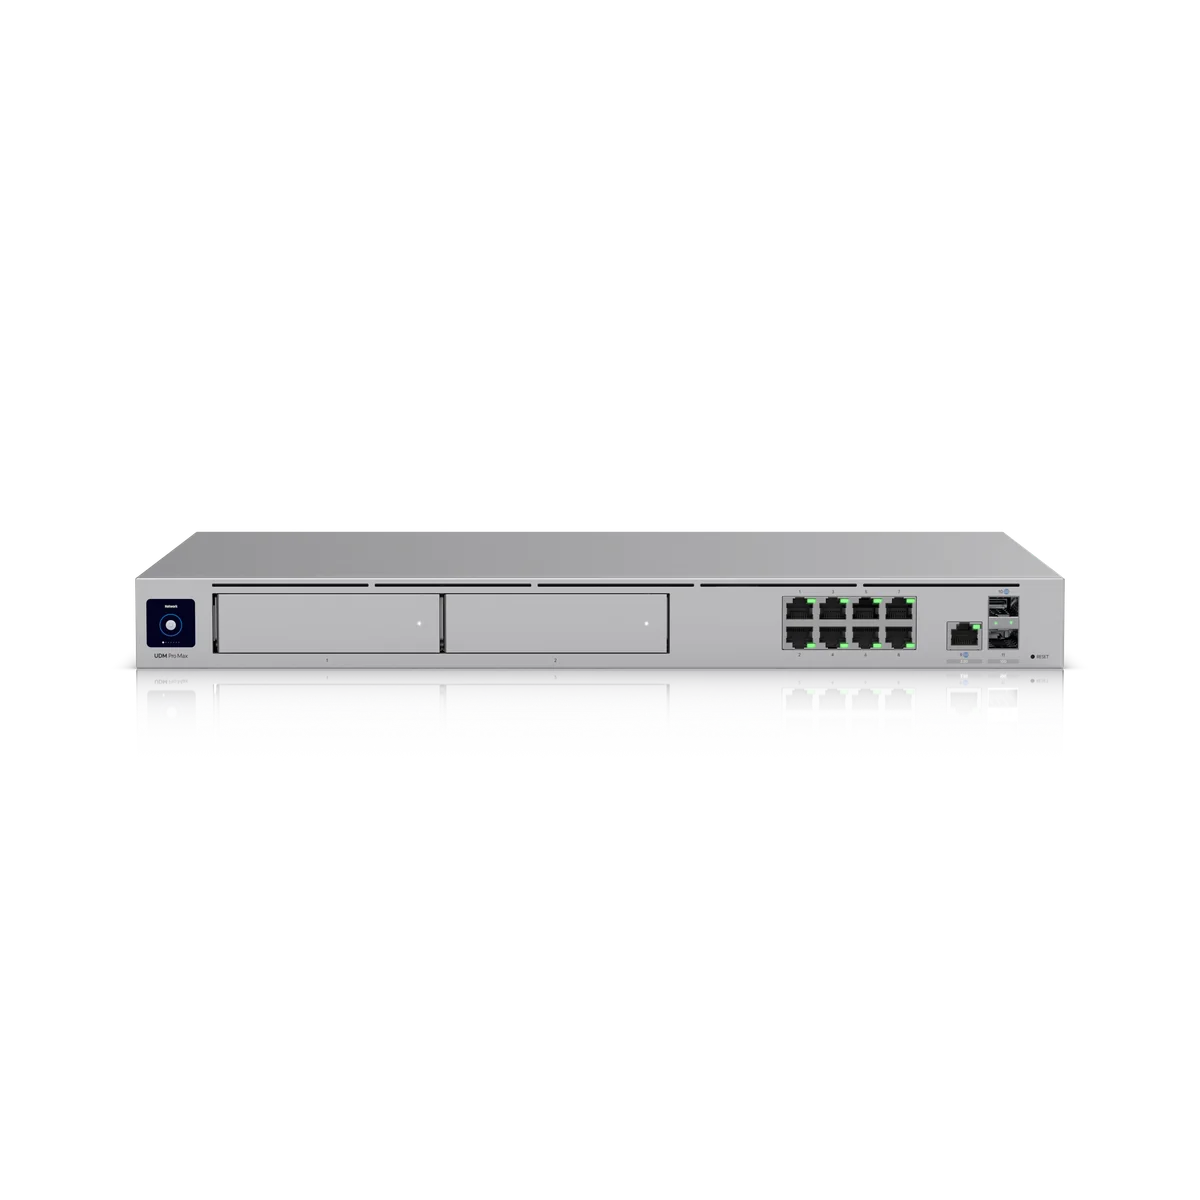
 Large ScaleRack
For larger sites with many UniFi devices and users, combining Network and Protect in a rack installation..
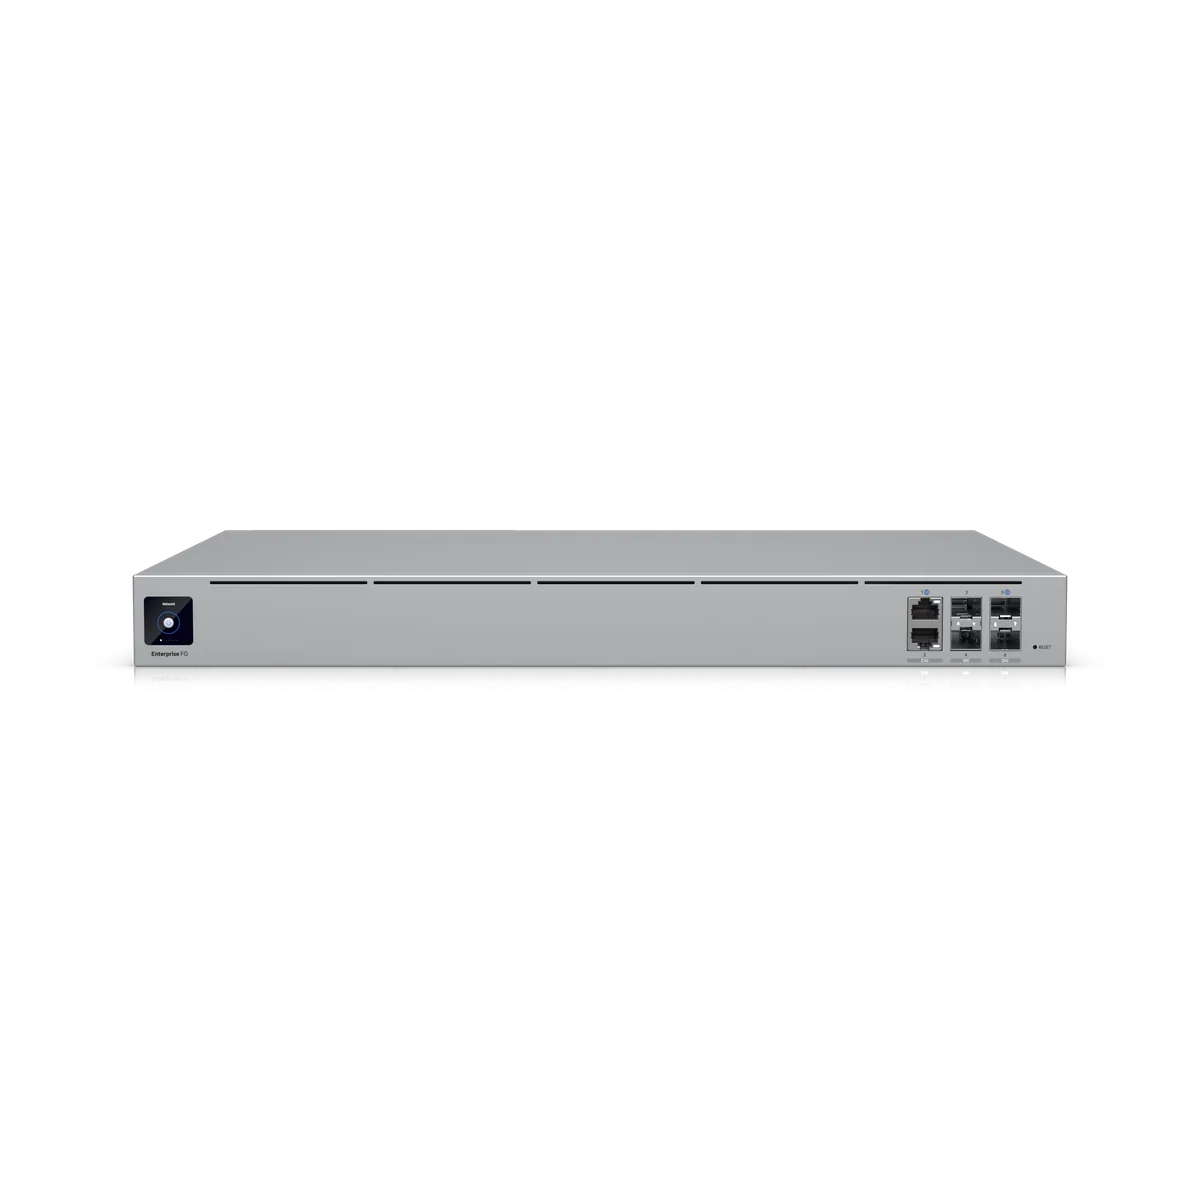 Enterprise25G
For central network boundaries with many clients, high security throughput and an explicitly designed high-availability architecture..

 Hyperscale25G
For very large UniFi environments where security throughput and the number of managed clients drive the selection..
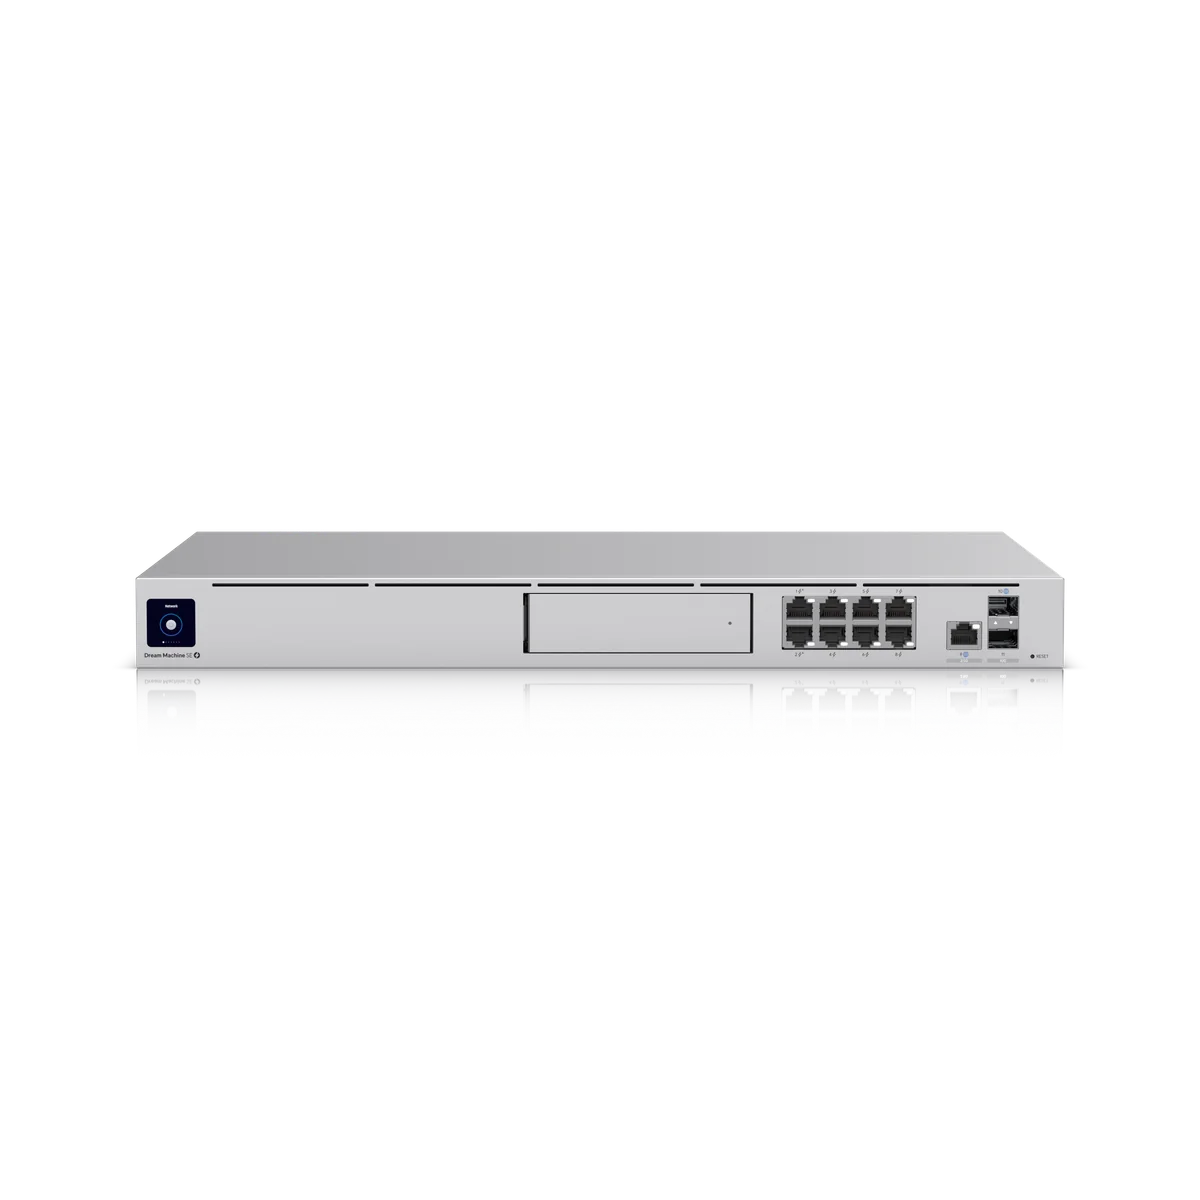 All in onePoE
For sites with a rack that want to combine a gateway, UniFi applications and a few directly powered PoE devices..
 CompactMulti-WAN
For small sites needing network management, a firewall and multiple internet connections in one compact device..
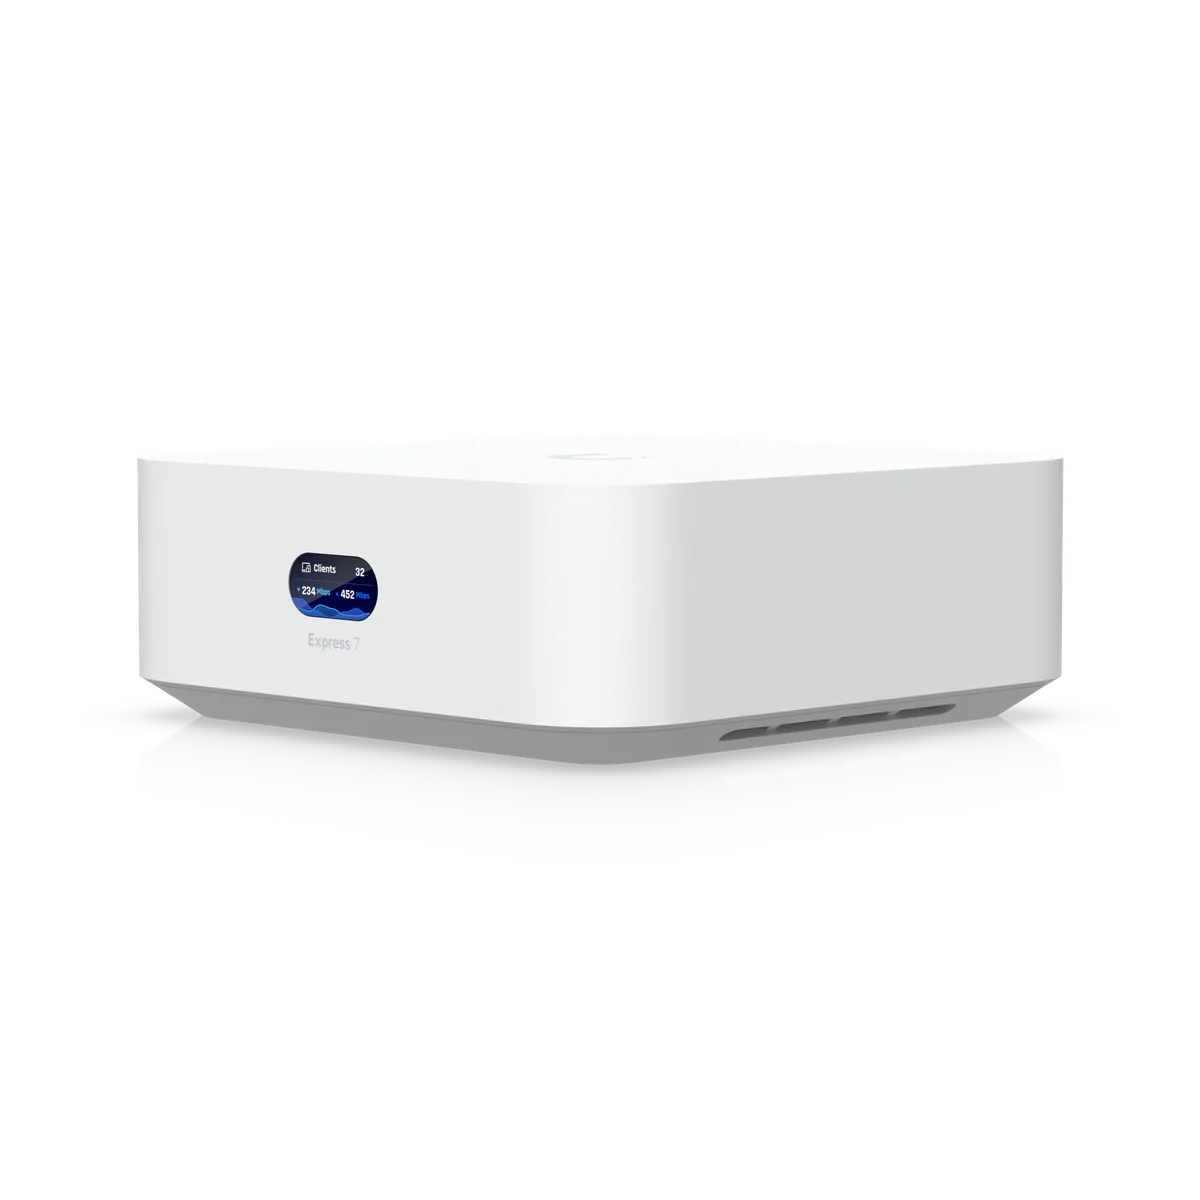
 WiFi Integrated10G
For very small sites combining a gateway and WiFi in one compact device, such as a single office..
 Product specifications according to official Ubiquiti pages. The specific design is based on bandwidth, security profile, applications and growth reserve.
Security is not a single product. It is created through segmentation, rules, identities, transparency and controlled operations.
Clear security zones for clients, servers, IoT, guests, cameras and management - with understandable rules instead of established exceptions.

Suspicious pattern detection, application visibility and traffic analysis help identify risks earlier and implement policies in a targeted manner.

Securely connect locations and employees - with Site Magic, IPsec, WireGuard and a centrally managed multi-site architecture.

The EFG combines high routing and IDS/IPS performance with advanced security features, high availability and fast 25G uplinks. We integrate it cleanly into your VLAN, WAN and identity architecture.
The right console depends on the number of users, bandwidth, protect load, availability, number of locations and growth reserve.
| Criterion | Cloud Gateway Max | Cloud Gateway Fiber | Dream Machine Pro Max | Enterprise Fortress Gateway |
|---|---|---|---|---|
| Typical use | Compact location | 10G ready SMB | Larger main location | Enterprise / Campus |
| Managed Devices | 30+ | 50+ | 200+ | 500+ |
| Concurrent clients | 300+ | 500+ | 2'000+ | 5'000+ |
| IDS/IPS | 2.3 Gbps | 5Gbps | 5Gbps | 12.5 Gbps |
| Storage | NVMe up to 2TB | NVMe up to 2TB | 2 × 3.5" HDD | External Protect NVR |
 01 / Segmentation
Device groups, identities and zones receive exactly the access they need - no more.
02 / ResilienceRedundant Internet lines, failover and, if necessary, shadow mode for critical environments.
 03 / Operation
Traceable changes, scheduled updates, configuration backup and proactive health control.
UniFi Network shows how stability, high availability and insights come together on a common platform.
Original video from UbiquitiSecure connections and clearly separated network segments start with the right architecture. novoSYS helps customers plan and implement their UniFi firewall.
 Gartenmann Engineering
 E-Display
 DemoSCOPE
 KULIQ Liquidationen
 Schubiger Möbel
 Beck
 RISAM AG
 Kinderheim Pilgerbrunnen
This depends, among other things, on Internet bandwidth, number of clients and devices, desired IDS/IPS performance, Protect cameras, redundancy and growth. We size with reserve, but without unnecessary oversize.
Yes. Depending on the requirements, Site Magic, IPsec, WireGuard or classic SD-WAN designs are used. We take routing, failover, address concept and central administration into account.
We analyze the existing environment, clean up rules and plan a controlled migration with a test and fallback concept.
We review requirements, existing topology and security goals and recommend the appropriate UniFi gateway architecture.
Request advice